Tel Aviv, Israel, September 30th, 2026, CyberNewswire
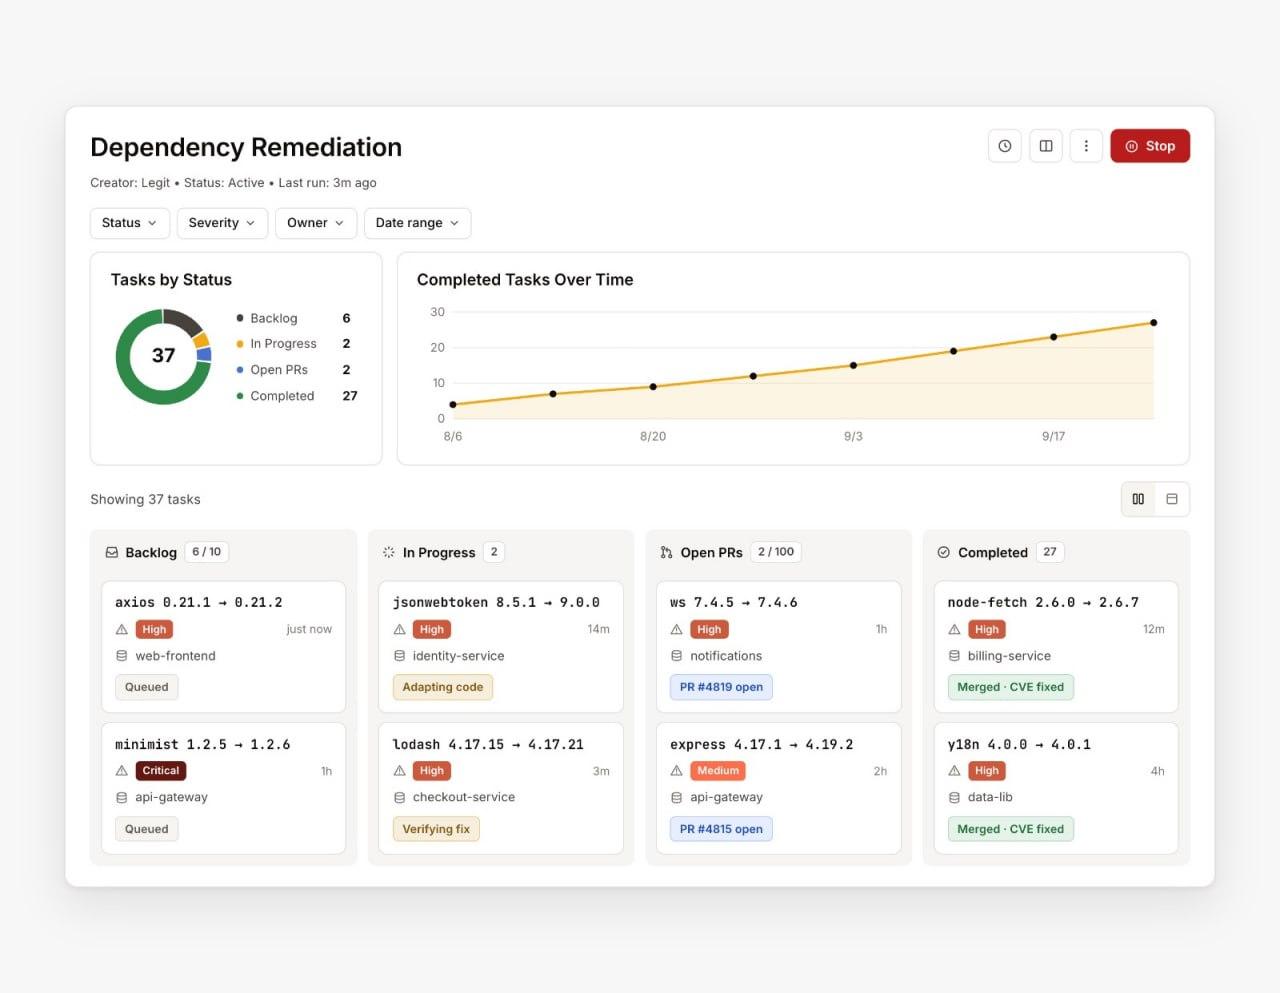
Legit Security today announced an expansion of its Agentic Remediation capability to cover vulnerabilities found in open-source dependencies, not just first-party code – enabling development teams to move from vulnerability detection to a verified fix without manual triage.
The expansion addresses a growing gap in application security: as AI-generated code accelerates software delivery, most modern codebases are made up largely of open-source dependencies, and every new package introduces potential exposure to known vulnerabilities. Traditional find-it, fix-it AppSec workflows, which rely on human teams working down a backlog, can’t keep pace with that volume – particularly when the vulnerable code isn’t in a company’s own codebase but several layers deep in a third-party package.
Legit’s Agentic Remediation previously focused on fixing static analysis findings in code written by a company’s own engineers. With this release, the same agent now takes on vulnerabilities introduced through dependencies , extending verified remediation to the other major source of vulnerabilities in modern software.
“The real challenge isn’t finding vulnerabilities anymore – it’s getting from finding to fix fast enough,” the company said, noting that AI-generated code has multiplied the volume of software shipping daily while attackers increasingly use AI to find and exploit those vulnerabilities faster than defenders can respond.
When pointed at a vulnerable dependency, the agent:
Every fix is re-scanned before a PR is opened, so developers receive a change that has already been verified rather than a suggested version to try.
When a fix requires crossing a major version boundary – where breaking API changes become a risk – the agent adds an AI-assisted analysis layer that evaluates how the specific repository uses the package and proposes the source code adaptations needed, validated against the real repository and package data.
Legit draws a clear distinction in these cases: the dependency fix itself is verified through re-scanning, like any other remediation, while the code adaptation for a major version jump is AI-assessed rather than independently verified. The company said the PR flags this distinction explicitly, so developers know what’s been verified and what warrants closer review before merging.
Legit positions the expansion as part of a broader effort to close the gap between detection and a safe, verified fix across both first-party code and open-source dependencies – the two primary sources of vulnerabilities in modern software – without relying on manual backlog triage.
Dave Howell Legit Security [email protected]
Your email address will not be published. Required fields are marked *