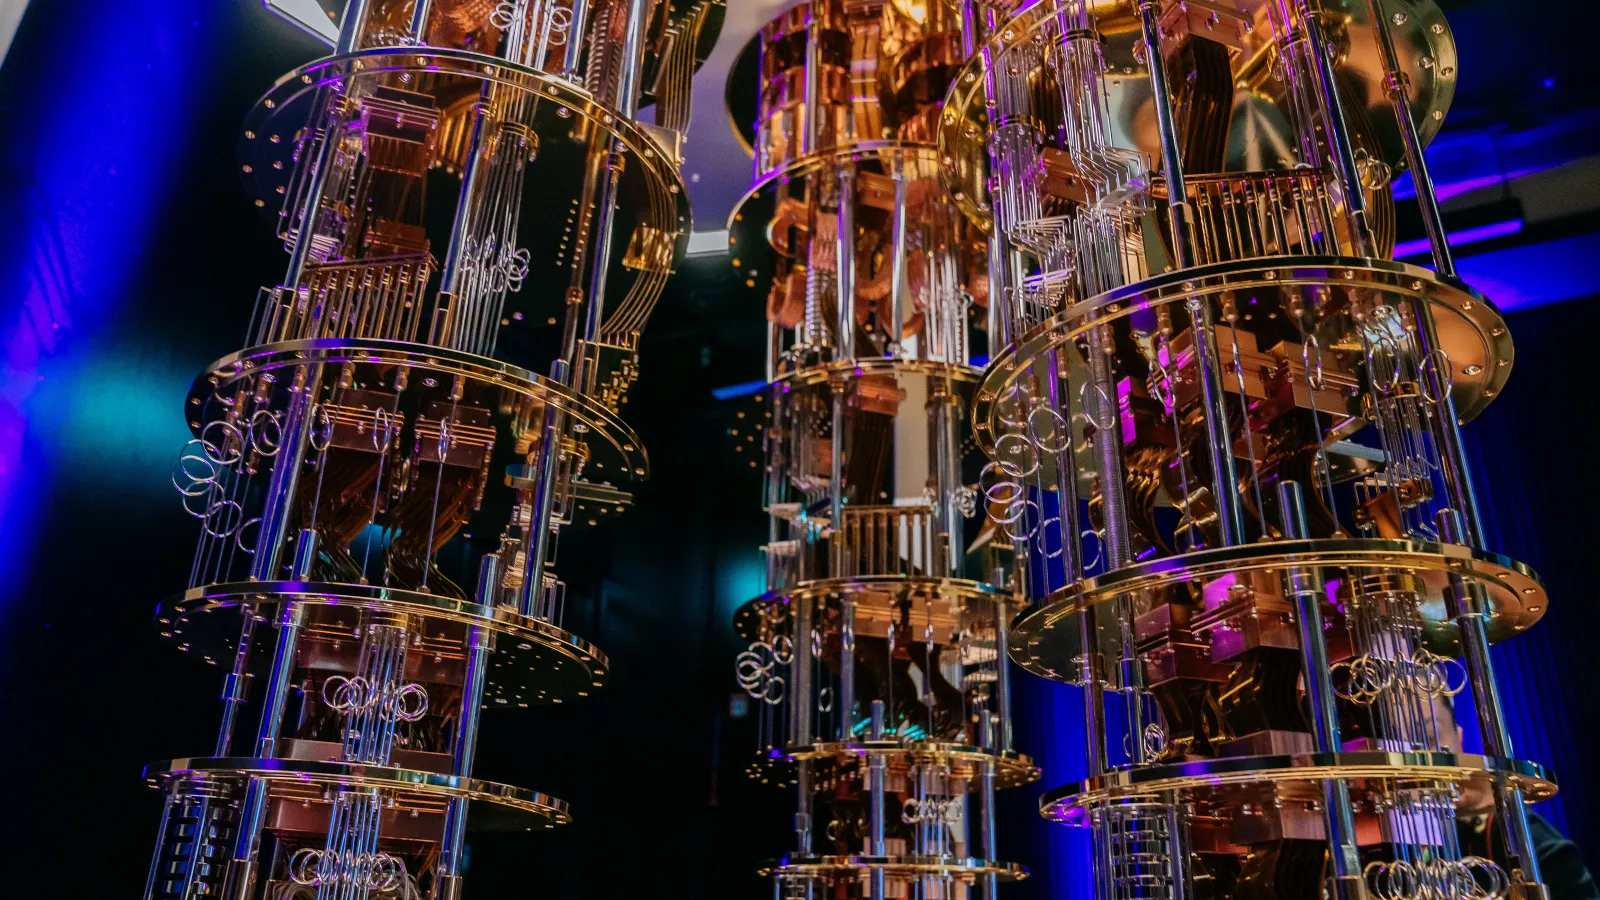
Auditors warned that agencies risked leaving sensitive data exposed to future decryption attacks.
U.S. government agencies are failing to prepare for the transition to post-quantum encryption, creating the risk that their sensitive data will still be vulnerable to decryption by quantum computers whenever those machines are deployed, according to the Government Accountability Office.
Experts are divided over when the advent of cryptographically relevant quantum computers (CRQC) will occur, but GAO bluntly declared in a report published Tuesday that “threats from a CRQC could have devastating impacts to federal systems reliant on vulnerable cryptography.”
Threat actors could use a quantum computer to decrypt stolen data or compromise sensitive communications between federal agencies. The same techniques could also undermine the trustworthiness of data transmitted over business networks and critical infrastructure . U.S. intelligence officials and private analysts say the Chinese government is likely building a vast trove of stolen U.S. data so that it can someday use a quantum computer to decrypt and exploit that data , a tactic known as “harvest now, decrypt later.”
The U.S. government has taken some steps to prepare for the looming global migration to post-quantum cryptography (PQC). The National Institute of Standards and Technology has standardized PQC encryption algorithms that can resist quantum computers’ code-breaking power. The Office of Management and Budget has directed agencies to prepare for the transition. The Cybersecurity and Infrastructure Security Agency (CISA) and its partners have published guidance documents for all organizations. But other agencies have been slow to act, according to GAO.
“Federal agencies recognize the quantum computing threat and have taken some actions to partially address it,” GAO said in its new report. “However, agencies have not fully carried out initial steps to prepare for this threat.”
Auditors looked at three steps that agencies need to take before adopting quantum-resistant encryption: inventorying their priority computer systems and the vulnerable cryptographic algorithms they use; identifying the funding needed to complete the transition; and testing PQC algorithms for compatibility with their systems.
By the end of the audit period, GAO said, only one of the 24 major federal agencies had completed the inventorying step, none had identified all necessary funding and none had fully tested PQC algorithms.
Most agencies have partially inventoried their systems and have identified some funding, according to the report, but almost none of the agencies have begun testing the new encryption algorithms.
Agencies struggled to build asset and algorithm inventories for several reasons, GAO found, including a lack of expertise with encryption, a lack of documented inventorying processes and a lack of automated inventorying tools. Only five of the 24 agencies used such tools to identify sensitive data protected with vulnerable algorithms. Of the 19 agencies that did not, officials from 15 of them said it was too early to use automated tools or they were waiting for CISA to recommend specific tools to them. (CISA told GAO that it was working with NIST to identify the best tools.)
Incomplete inventories and a lack of information about what new tools would cost made it difficult for agencies to prepare budget estimates for the PQC transition, according to the GAO report. The Office of the National Cyber Director said the immaturity of the PQC vendor landscape was “the biggest factor” delaying funding estimates.
“As more commercially available products with PQC become available,” GAO auditors wrote, “vendors will be positioned to provide agencies with more accurate cost data.”
Only one agency had begun the process of preparing to test PQC algorithms, but according to GAO, that agency had only “conducted market research to identify candidate vendor implementations of PQC” in software that it planned to test. The agency had not begun the actual testing. None of the other 23 agencies had completed any work toward algorithm testing. Sixteen of those agencies told GAO that it was too early for testing because most vendors still hadn’t incorporated the new algorithms into their products.
“Until agencies develop and implement such plans,” GAO said in its report, “they will not be well-positioned to identify and quickly replace certain systems (e.g., legacy systems and custom software) that may not support PQC.”
The agency acknowledged that there is no consensus on when the first CRQC will be built, but it warned that “the impact of such a computer on unprepared federal systems could be catastrophic to the nation’s economy and security.”
In a version of the report not publicly released, GAO recommended 89 actions that CISA and other agencies could take to increase their preparedness. Of the 23 agencies to which GAO assigned recommendations, only 12 fully agreed to implement them. “We continue to believe that all of the recommendations made in the sensitive report are warranted,” GAO said.